Loading Yahya Hcini's Portfolio

Web Security Researcher & Bug Bounty Hunter

Mapping the attack surface.

Open to security research & freelance work

Web Security Researcher Bug Bounty Hunter Web Pentester

I focus on bug bounty hunting and web application penetration testing — authentication, authorization, access control, APIs, and business logic. A full-stack MERN background means I understand how these applications are actually built, which shapes how I test them.

+3
Years Researching & Building
+58
Vulnerabilities Documented
+52
Applications & APIs Tested
About Me

The researcher behind the findings

Security-focused, full-stack grounded, and always testing assumptions
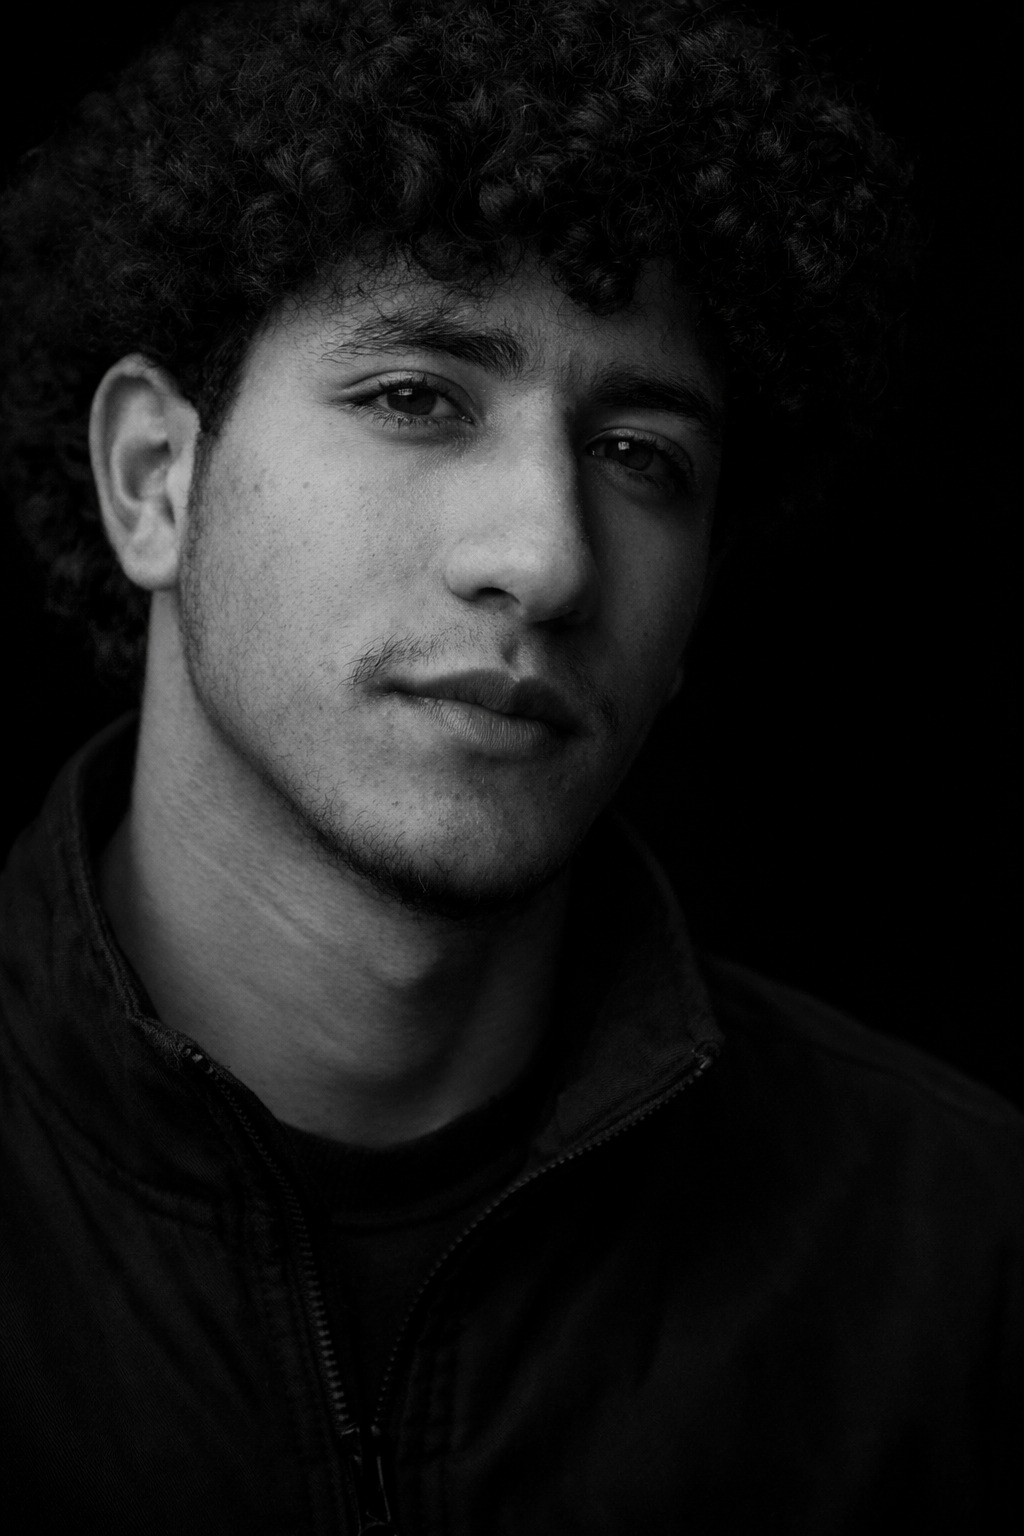
Yahya Hcini - Web Security Researcher and Bug Bounty Hunter in Tunisia
+3
Years of research
+58
Vulnerabilities found
Open to work

"Understand how it works. Then understand where it breaks."

I'm Yahya Hcini, a web security researcher from Sidi bouzid, Tunisia focused on bug bounty hunting and web application penetration testing. My background in full-stack development gives me a practical understanding of how modern web applications and APIs are actually built — which I apply directly when researching where their security assumptions break.

My research covers authentication, authorization, access control, APIs, business logic, XSS, SQL injection, CSRF, SSRF, and GraphQL security. I conduct authorized security research through bug bounty programs on HackerOne and Bugcrowd, alongside hands-on security labs and independent research — and I build tooling like Y-Scope to support that work. Open to remote security research and pentesting opportunities worldwide.
Bug Bounty Hunter
API & GraphQL Security
Full-Stack Foundation
Security Tool Builder
Journey
2023 / 2024
Started Full-Stack Development
Learned the MERN stack from the ground up and built early, general-purpose projects.
2025
Moved to Professional, Security-Focused Websites
Started building production-grade websites and shifted focus toward making them properly secure, not just functional.
2026 — Present
Started the Bug Bounty Journey
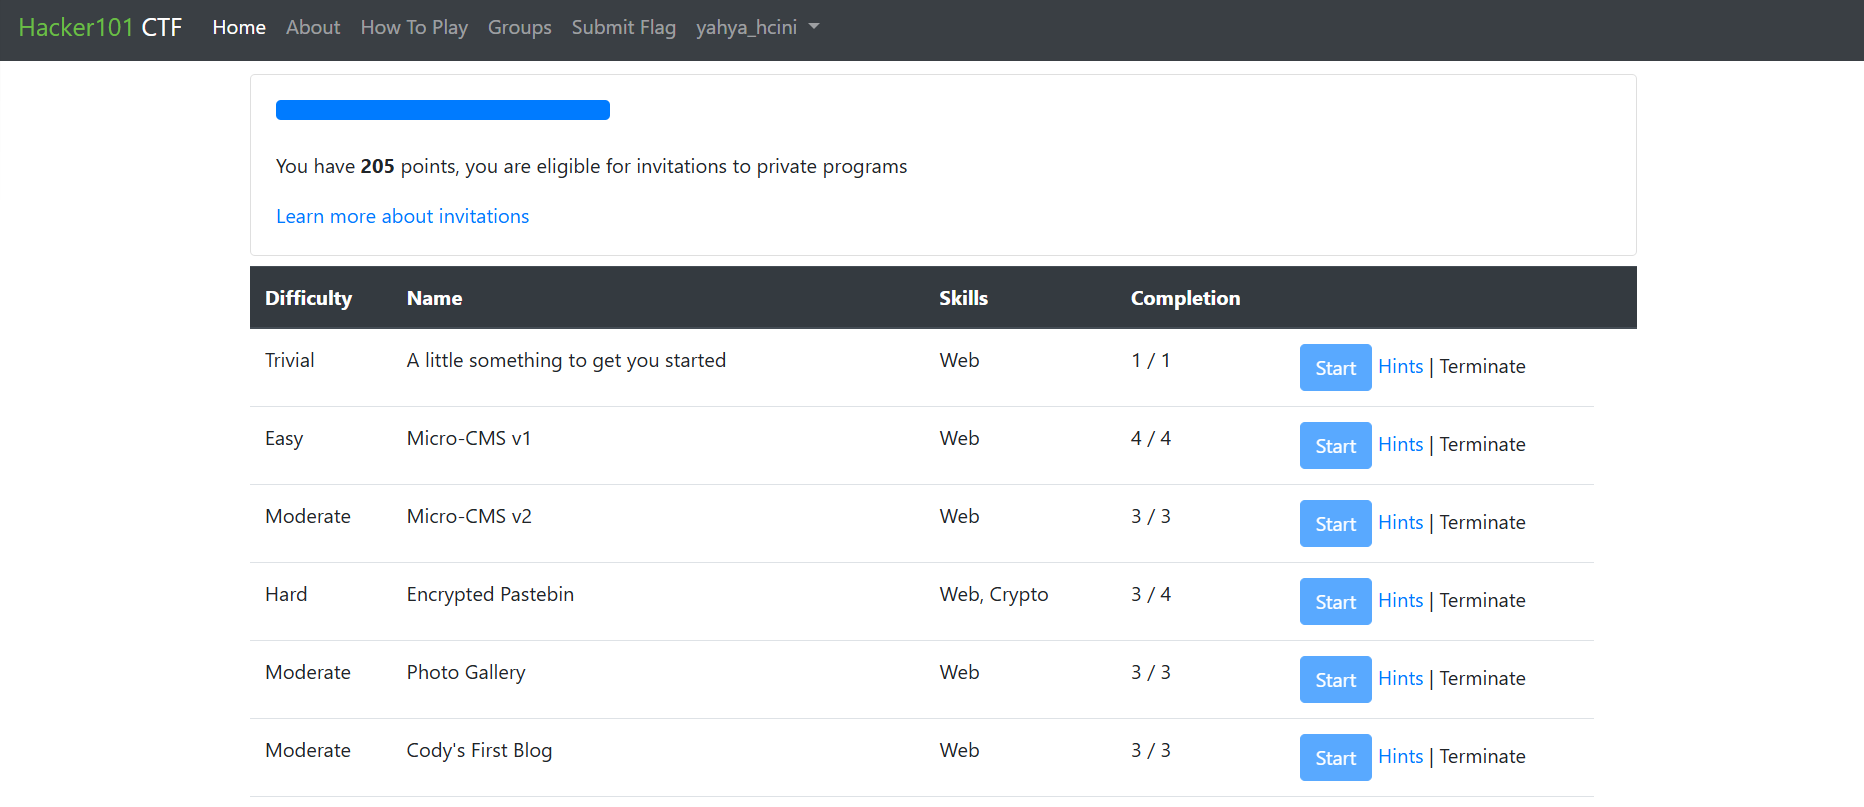
Began bug bounty hunting in April 2026 and has been diving deeper into it since — Hacker101 CTF,HackerOne, Bugcrowd
What I Do

My Services

Security research and full-stack engineering, grounded in how applications are actually built

Web App Penetration Testing

Authorized security assessments of web applications and APIs, focused on where real breaches happen — not just automated scan output.

  • Authentication & authorization testing
  • Access control & business logic review
  • OWASP Top 10, GraphQL & API testing

Bug Bounty & Vulnerability Research

Independent research and coordinated disclosure through public bug bounty programs, backed by a structured recon-to-report methodology.

  • Recon & attack-surface mapping
  • Coordinated disclosure via HackerOne / Bugcrowd
  • Detailed reports with reproducible PoCs

Secure Full-Stack Development

MERN stack applications built with a security researcher's eye — the same background that shapes how I break applications also shapes how I build them.

  • React / Node.js / Express / MongoDB
  • Secure authentication (JWT) & API design
  • E-commerce platforms & custom dashboards
My Work

Featured Projects

Security research and bug bounty work, alongside the full-stack engineering that informs it.

Y-Scope Reconnaissance Framework Security
v1.0.0 LIVE

Y-Scope — Recon Framework

A modular reconnaissance framework for authorized security testing and bug bounty research. v1.0.0 covers passive subdomain discovery, certificate transparency enumeration, DNS resolution & wildcard detection, active subdomain discovery, HTTP/HTTPS probing, and result deduplication — built to expand into a broader attack-surface framework over future versions.

Python Recon DNS Enumeration Cert Transparency HTTP Probing
Hacker101 CTF Writeups Security
+17 LABS • +58 VULNS

Hacker101 CTF — Complete Writeups

17 capture-the-flag challenges solved from Hacker101's CTF platform. 58 vulnerabilities documented with step-by-step exploitation guides, payloads, and root cause analysis. Covers OWASP Top 10 and beyond — SQLi, IDOR, XSS, SSRF, GraphQL injection, file upload RCE, XXE, PRNG cryptanalysis, and mobile APK reversing.

SQLi IDOR XSS SSRF
Burp Suite Ghauri ffuf feroxbuster jadx GraphQL JWT
BugBountyPlaybook Security
Research Notes

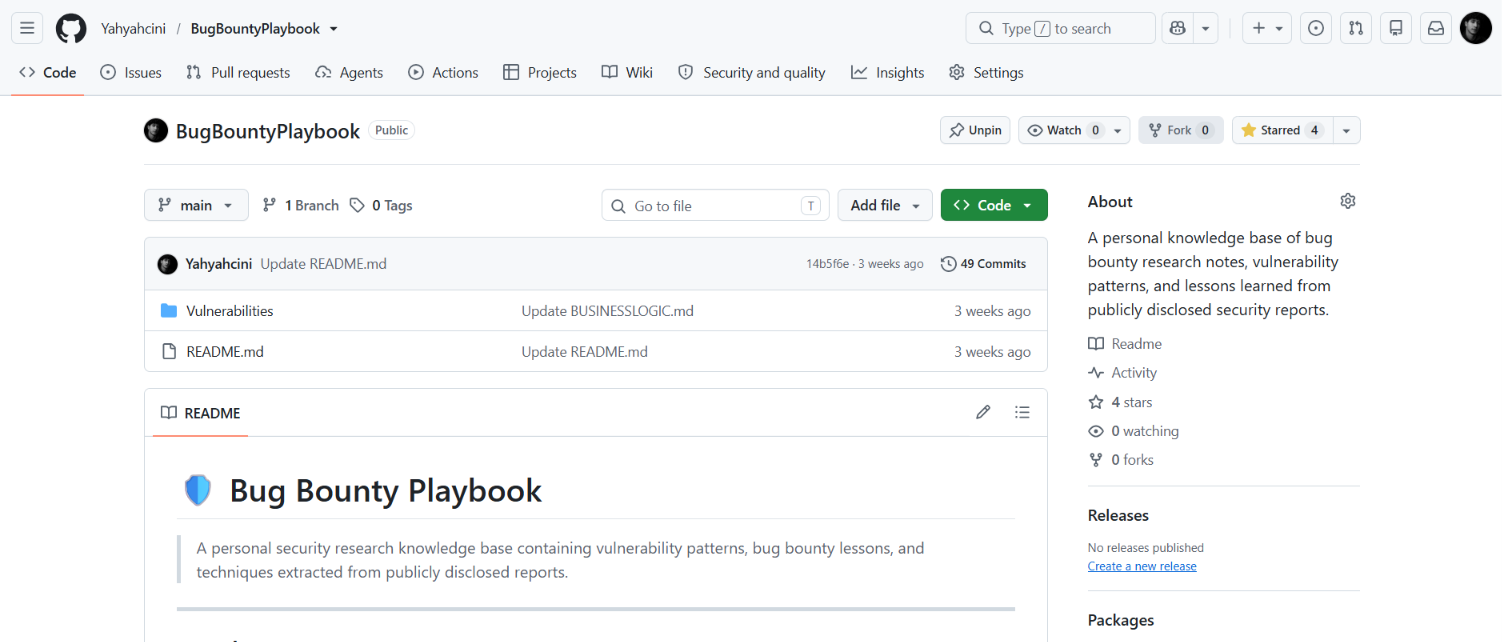
BugBountyPlaybook

A personal knowledge base covering vulnerability patterns, research methodology, and lessons learned from publicly disclosed security reports — built as a working reference for my own bug bounty research.

Methodology Vulnerability Patterns Case Studies
Portswigger Labs Security
+32 labs completed

PortSwigger Labs Solutions

A complete collection of PortSwigger Web Security Academy lab solutions with detailed write-ups and exploit scripts across the OWASP vulnerability spectrum.

PythonBurp SuiteSQL InjectionXSS
Security Notes and Concepts Repository Security
Research Notes

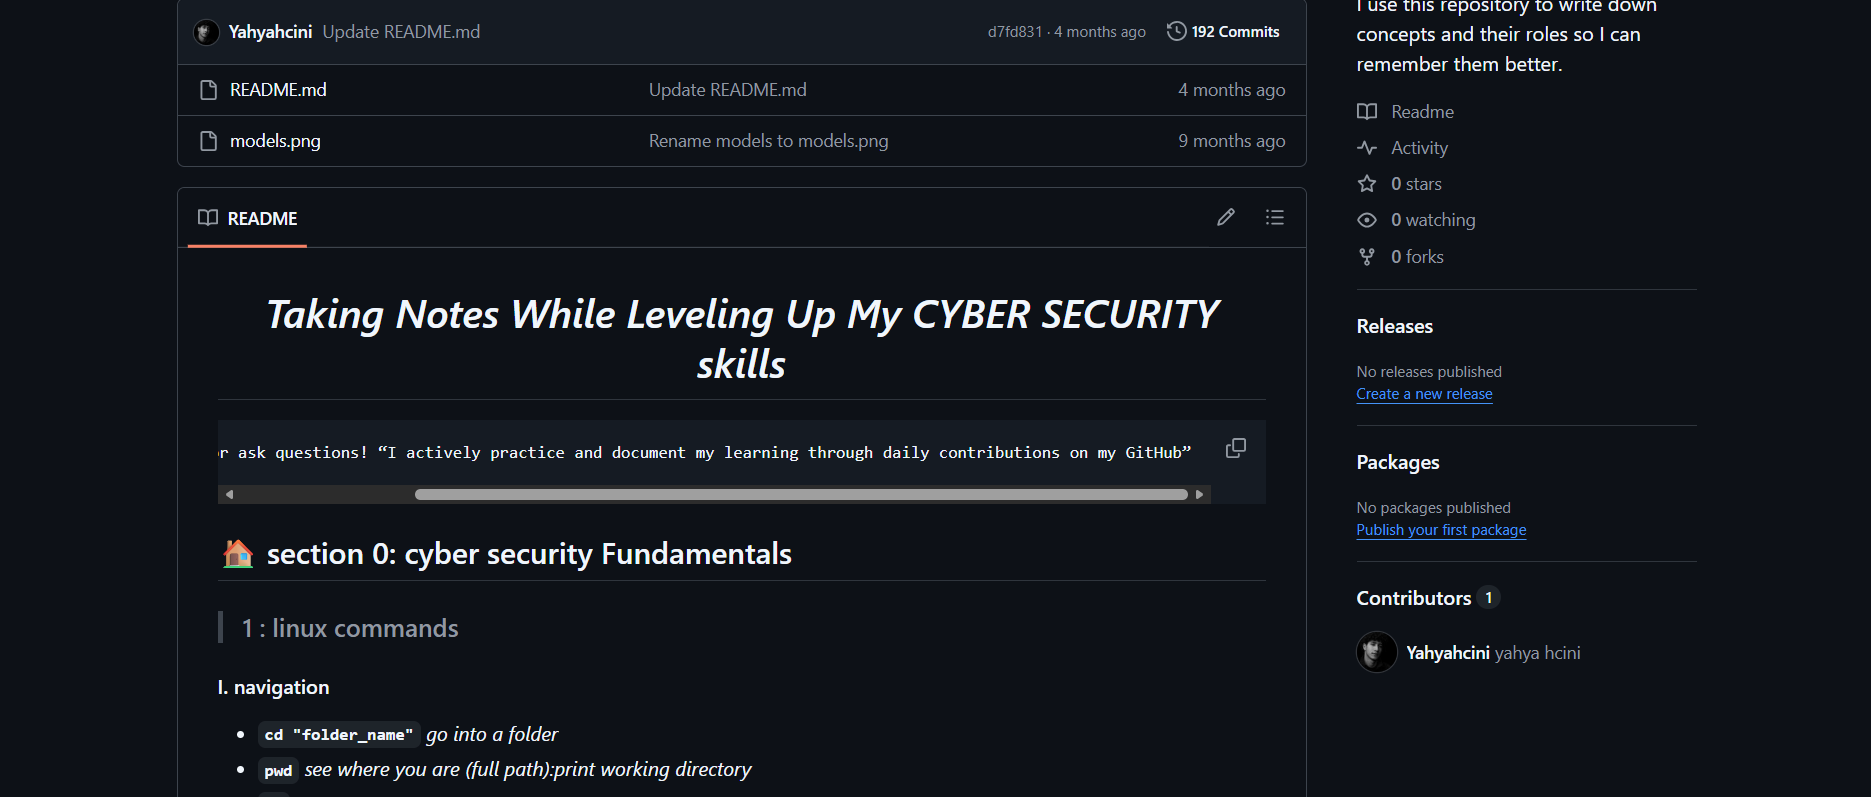
Security Concepts & Notes

A running personal reference where I write down security concepts, Linux commands, and the role each one plays — a working memory aid built while learning, kept up to date as the research continues.

Linux Security Concepts Reference Notes
LISATERRA Platform Web Dev
✨ COMPLETE PLATFORM

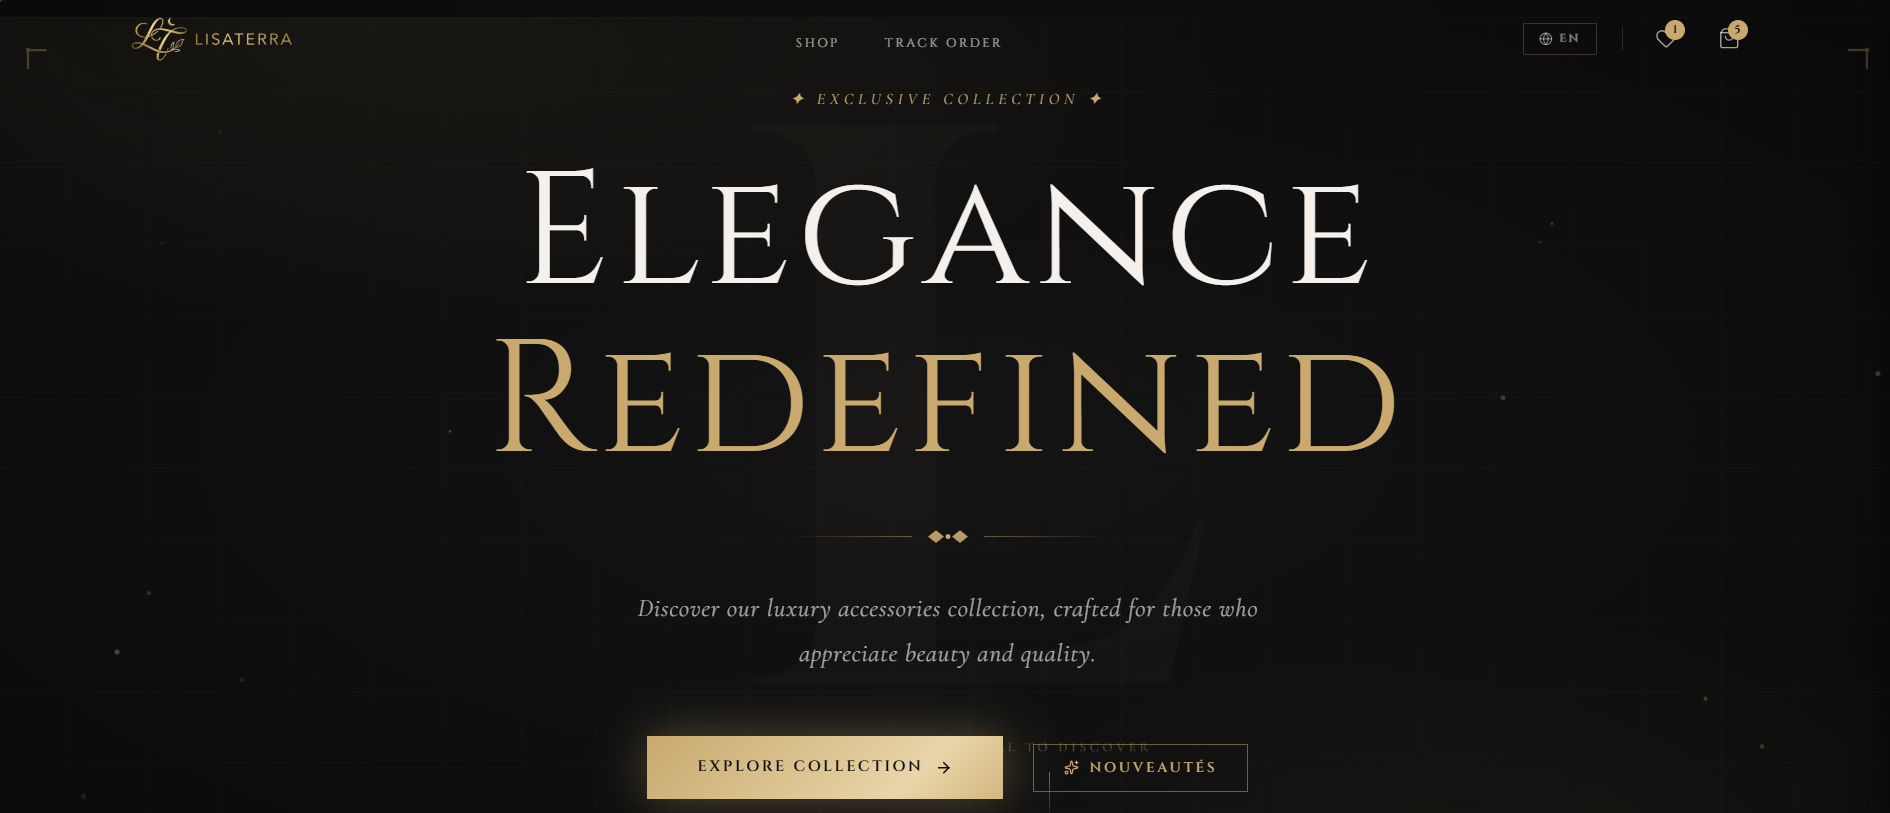
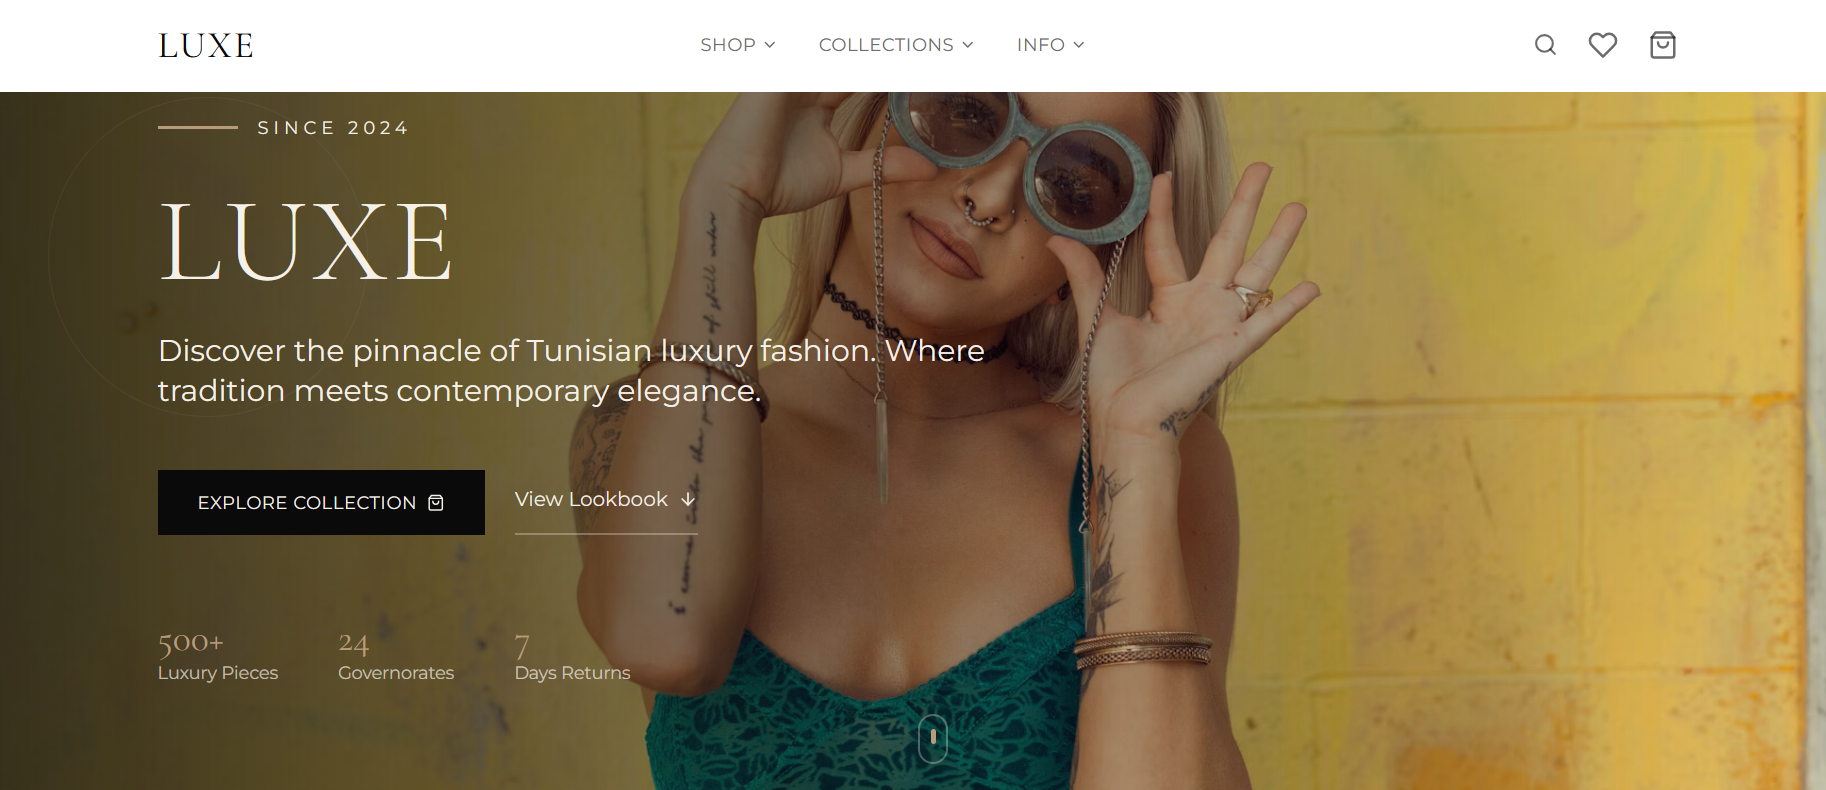
LISATERRA — Luxury Accessories

Complete luxury e-commerce platform with an AI shopping assistant (Groq API, LLaMA 3.3 70B), real-time inventory management, and enterprise-grade security. Features include smart wishlist, automated order tracking, and an admin dashboard with complete CRUD operations.

React 19 Vite Node.js Express MongoDB Atlas Groq AI Agent JWT Auth Zustand Tailwind CSS Framer Motion Cloudinary
ISIMM Archive Web Dev
Live

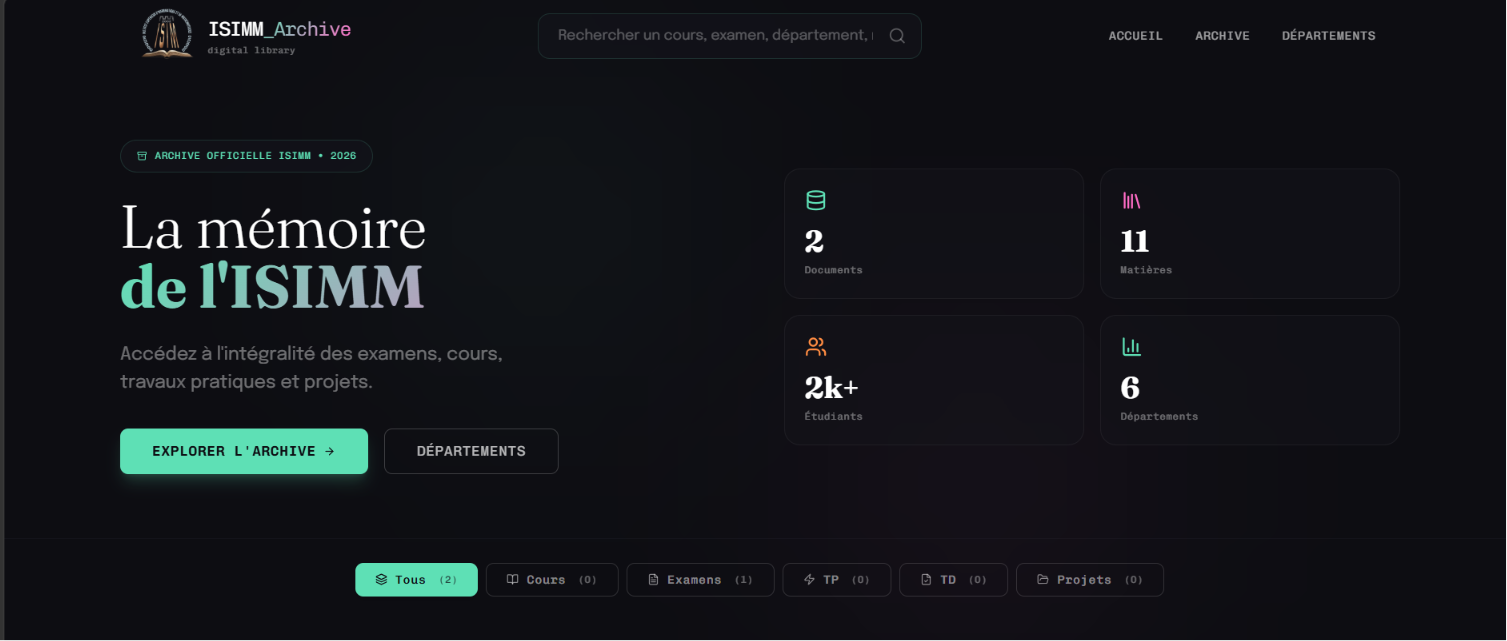
ISIMM Archive — Digital Library

A free, centralized digital library for ISIMM students — exams, courses, TPs, TDs, and projects in one place, with smart search, multi-filter browsing, a PDF viewer, and a student submission system with admin moderation.

ReactStrapi CMSTailwind CSSPostgreSQL / SQLite
Premium E-Commerce Platform Web Dev
✨ COMPLETE PLATFORM

Premium E-Commerce Platform

Production-ready e-commerce solution with advanced product management, secure application design, and a Strapi CMS backend.

ReactStrapi CMSModern Stack
Fripe E-commerce Web Dev
Live

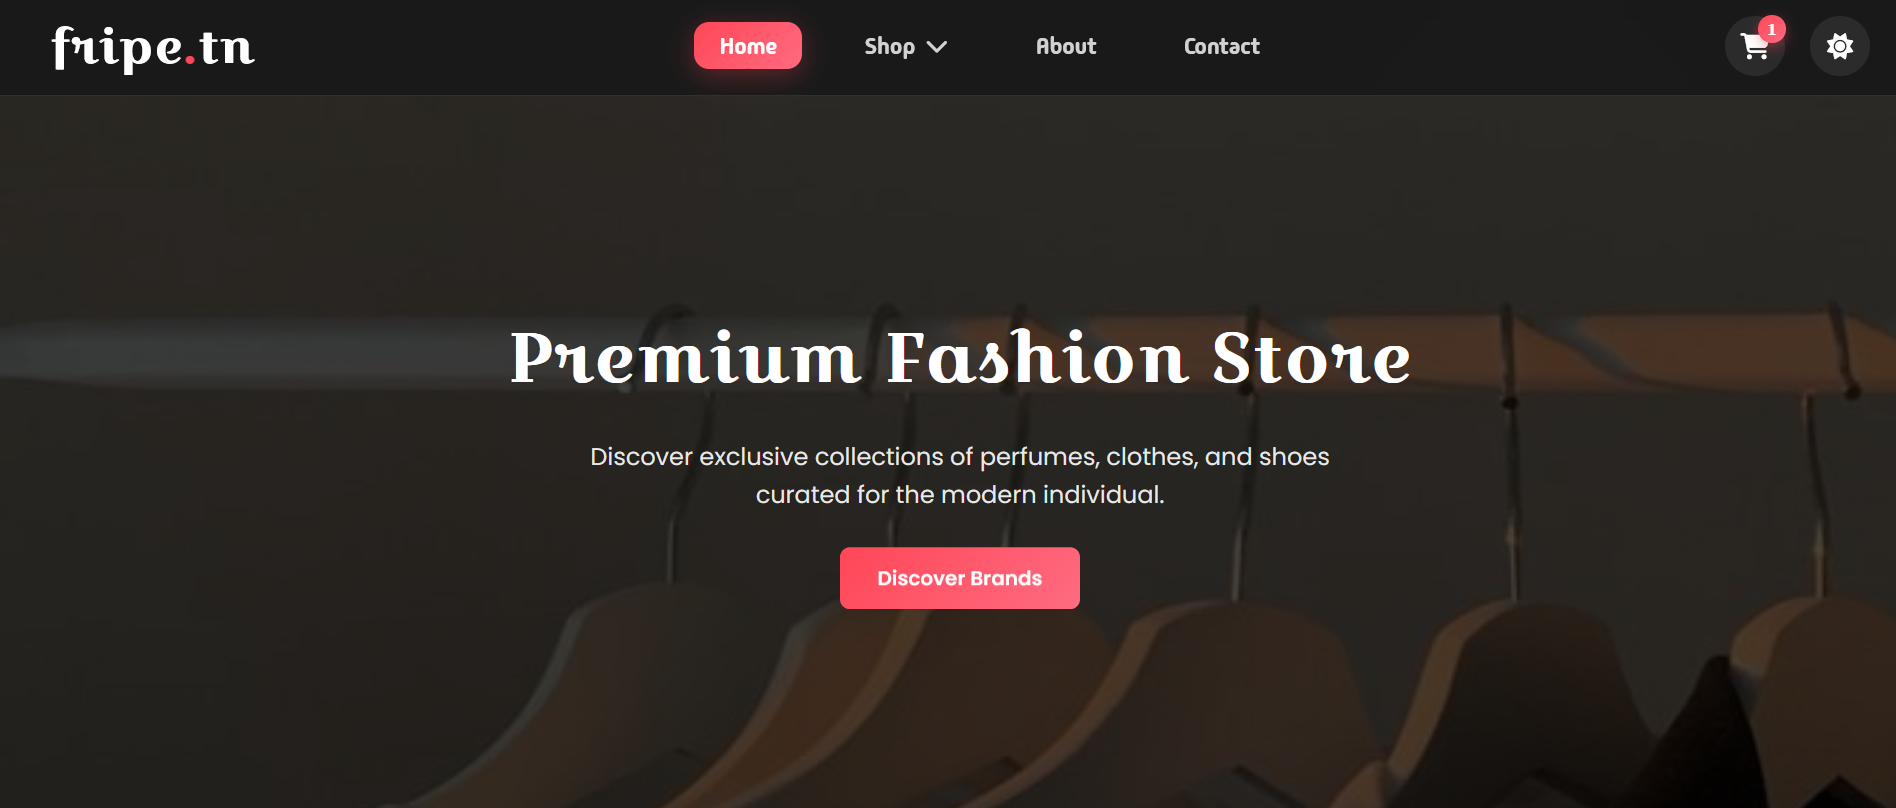
Fripe E-commerce Platform

Complete clothing store with secure authentication and a CMS-based management system.

HTML5CSS3JavaScriptStrapi CMS
Secure Task Manager Web Dev
Complete

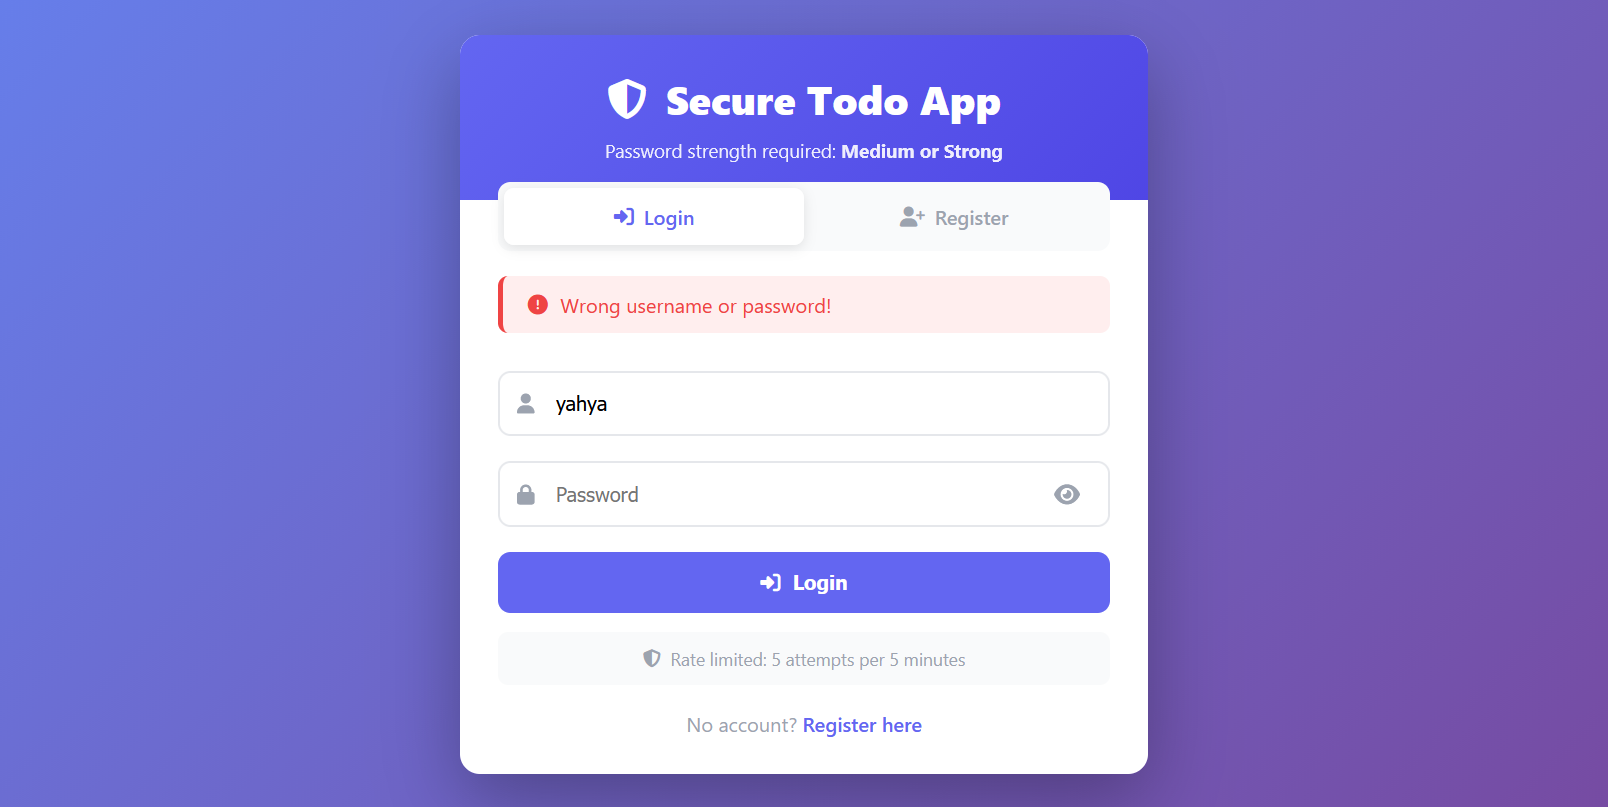
Secure Task Manager

Full-featured task management application with secure authentication, role-based access, and optimized database operations.

PHPMySQLCSS3Security
Expertise

Technical Skills

Security research first, full-stack engineering behind it — explored like a terminal

Core Stack Web App Pentesting Bug Bounty Hunting GraphQL Security React / Node MERN Burp Suite Python Tooling
yahya@sec ~ /skills +55 skills loaded
$ cat skills.json | grep --security --webdev

Security Research & Pentesting

Web application security research, vulnerability classes, and the recon/testing tools used to find them.

Vulnerability Classes & Methodology
Recon & Testing Tools

Web Development

Full-stack MERN engineering — the foundation my security research builds on.

Frontend
Backend

Databases & DevOps

Schema design, deployment pipelines, and lab infrastructure.

Databases
DevOps & Tooling

Languages & AI

Languages I write with, and the AI/automation work layered on top.

Programming Languages
AI & Automation
Get In Touch

Let's Work Together

Have a security research collaboration or a web project in mind? Reach out.

Email

hciniyahya89@gmail.com

Response within 24 hours

WhatsApp Business

+216 94 619 928

Start Chat

Location

Sidi bouzid, Tunisia

Remote work worldwide

Availability

Monday - Friday

9:00 AM - 6:00 PM CET

Thank you! Your message has been sent successfully.
Please enter your name
Please enter a valid email
Please select an inquiry type
Please add more details (minimum 10 characters)